Loading Howl Media Labs
Preparing the page and animations...
Loading Howl Media Labs
Preparing the page and animations...
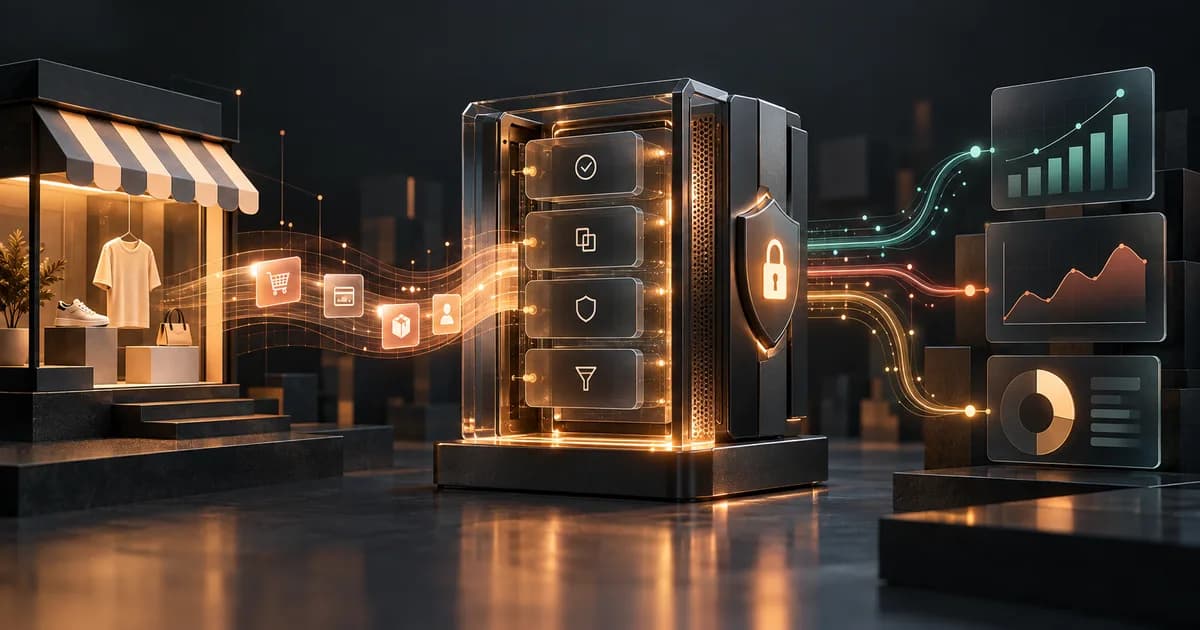
Shopify brands should adopt server-side tagging only after browser-side ecommerce events, consent signals and order IDs are reliable. A server container can improve control, performance and data quality, but it cannot repair ambiguous event definitions. Start with a tracking audit, route one validated event stream through a first-party endpoint, deduplicate purchases and reconcile every result to Shopify orders.
Server-side tagging is often sold as a cure for missing conversions. That framing is too broad. The architecture changes where measurement requests are processed; it does not decide what a purchase means, whether consent was valid, or whether a platform-attributed order was incremental.
Google's server-side tagging introduction describes a server container that receives requests, interprets them through clients and then processes tags, triggers and variables before sending approved data onward. The server runs in infrastructure controlled by the business rather than executing every destination's logic directly in the shopper's browser.
For Shopify, the practical architecture is:
This is not the same as moving the entire storefront or checkout onto a custom server. It is a measurement-routing layer.
Complete site live in 4–5 weeks
See how we shipped a complete tourism site in 4–5 weeksRead it →
Use five readiness gates before approving implementation.
| Gate | Evidence required | Stop condition |
|---|---|---|
| Event design | Written definitions for viewitem, addtocart, begincheckout, purchase and refund | Different tools use different definitions |
| Identity | Stable product IDs, order IDs and currency rules | IDs change between browser, Shopify and analytics |
| Consent | Documented banner or CMP behavior by market and purpose | Consent state cannot be reproduced in QA |
| Reconciliation | Daily comparison of Shopify net orders and analytics purchases | No owner or tolerance for discrepancies |
| Operations | Named owner, monitoring and rollback plan | Nobody can diagnose a broken release |
Google's why and when guide identifies privacy control, browser performance and data quality as the main reasons to consider the architecture. None removes the need for good event design.
If these gates fail, complete the Shopify GA4 conversion tracking audit first. HML's Shopify analytics case study shows why duplicate and missing events must be fixed before more infrastructure is added.
Shopify's pixels and customer events documentation distinguishes app pixels from custom pixels. Shopify recommends using an app pixel when a suitable integration exists because app pixels include platform-managed security and updates. Custom pixels are the developer-controlled fallback when an app pixel does not meet the requirement.
That creates three common implementation paths:
| Path | Best fit | Main risk |
|---|---|---|
| Supported app pixel | Standard platform integration and limited custom logic | Assuming the app's event mapping matches the business definition |
| Custom pixel plus web GTM | Controlled custom events and routing | Unsupported code, maintenance and accidental duplication |
| Web GTM plus server GTM | Mature measurement team requiring first-party routing and transformations | Added hosting, monitoring, consent and QA complexity |
Do not run all three for the same purchase event without a deliberate deduplication design. Shopify explicitly warns merchants to remove or modify existing pixel code before adding a custom pixel so events are not counted twice.
Server-side tagging does not remove consent obligations. Google's server-side consent mode guide says the consent solution operates in the web layer: the user's choice is collected in the browser, included with the request and interpreted by consent-aware tags in the server container.
Shopify's customer privacy documentation also notes that manually installed third-party pixels may need custom logic to honour consent. Configuration can vary by market, and automated settings are not a substitute for legal advice.
A QA plan should test at least:
The first-party data glossary explains the ownership concept. First-party collection still requires purpose limitation, transparency and appropriate consent.
Use one stable transaction identifier from checkout through every approved destination. Google's transaction ID guidance says a unique transaction_id should be sent with ecommerce purchases so GA4 can deduplicate repeat web events and process refunds correctly.
Create a purchase contract before implementation:
Never send an empty transaction ID. Do not manufacture a new ID independently in the browser and server; that prevents deduplication.
Consider a fictional Indian apparel brand migrating one purchase stream to server-side GTM. The figures are synthetic and are not a benchmark.
| Daily checkpoint | Browser-only baseline | Server-side test | Shopify ledger |
|---|---|---|---|
| Gross purchase events | 1,080 | 1,034 | 1,020 orders |
| Duplicate IDs | 44 | 3 | 0 duplicate orders |
| Empty transaction IDs | 12 | 0 | 0 |
| Cancelled orders | Not identified | Reconciled next day | 38 |
| Net purchases after rule | 1,024 | 993 | 982 net orders |
| Difference from ledger | 4.3% | 1.1% | Reference |
Method: export order ID, gross value, currency, cancellation and refund state from Shopify; export the corresponding analytics purchase records; compare unique IDs rather than daily totals alone; investigate every duplicate, empty ID and currency mismatch; and calculate the difference only after applying the same cancellation window. Run browser-only and server-side paths in a controlled QA environment before production, then use a short overlap period with clearly separated test destinations.
The lower discrepancy in this example does not prove that server-side tagging always improves accuracy. It shows how a team would test the claim. The remaining 1.1% needs an explanation before the server result is accepted as truth.
Use a staged release:
Use the conversion-rate calculator to quantify funnel changes, but do not attribute a change to the tagging release without controlling for traffic mix, stock, promotions and site changes. The Shopify analytics session baseline guide provides the adjacent session-level reconciliation framework.
A useful audit should not end with “install server-side GTM.” It should deliver:
If the store cannot reconcile purchases or identify which pixel owns each event, request a Shopify measurement architecture audit from HML's website development team. The first deliverable should be evidence and a migration plan—not a new container deployed on top of an unknown stack.
Reviewed by rajkumar-tahalani on 30 September 2026. Access dates are shown for time-sensitive references.
Website Development
Shopify Analytics Session Update: A Baseline Reset Guide for Indian D2C
Website Development
Shopify GA4 Conversion Tracking Audit for Indian D2C Brands
Free Tool
AOV Calculator
Find your average order value and its upside.
Case Study
4.5x Total ROI
How a Premium Bespoke Tailoring Brand Achieved 4.5x ROI Across Digital Channels
We help Indian D2C brands grow with performance marketing, AI automation, and AEO-ready content. Book a free strategy call and we'll show you where the biggest wins are.